Enterprise Security &
Data Protection SLA
We build security into the foundation: CSRF/XSS protection, encrypted environment vaults, Cloudflare SSL edge caching, and isolated cloud hosting.
Navigation Index
1. Hardened Application Architecture
All StackShooter Python Django & React codebases are engineered against OWASP Top 10 security threats: automatic CSRF protection tokens, parameterized SQL queries against injection attacks, strict HTML/XSS sanitization, and enforced HTTP Content Security Policies (CSP).
2. Data Encryption at Rest & Transit
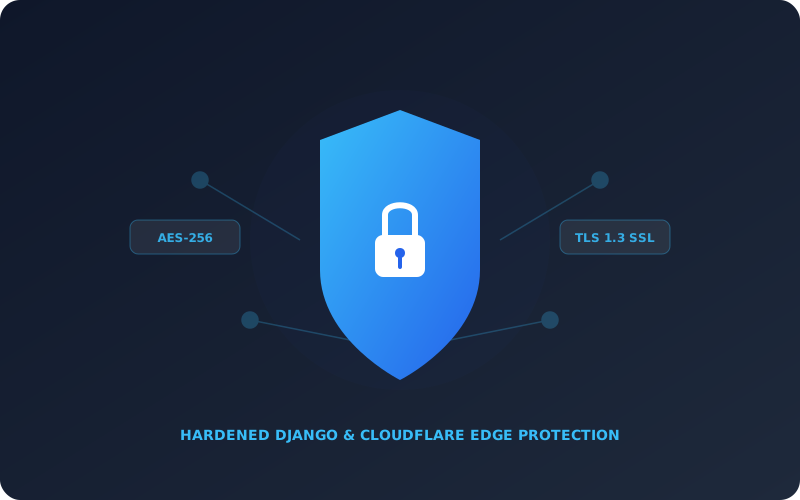
Client databases (PostgreSQL/MySQL) and cloud storage buckets use AES-256 bit encryption at rest. All network data transmissions between client applications, API servers, and third-party gateways are strictly encrypted via TLS 1.3 SSL edge proxy protocols.
3. Isolated Cloud Environments & Access Controls
Production staging and live web applications are deployed inside isolated AWS / DigitalOcean Virtual Private Clouds (VPC). API tokens, database passwords, and third-party keys are managed through encrypted environment secret vaults — never exposed or hardcoded into source repositories.
4. Vulnerability Audits & Disclosure SLA
We execute automated static code analysis (SAST) and dependency vulnerability checks before every production deployment. To report a security vulnerability or request a security SLA evaluation, contact our engineering team at support.stackshooter@gmail.com.